What Is Data Loss Prevention (DLP) Software?
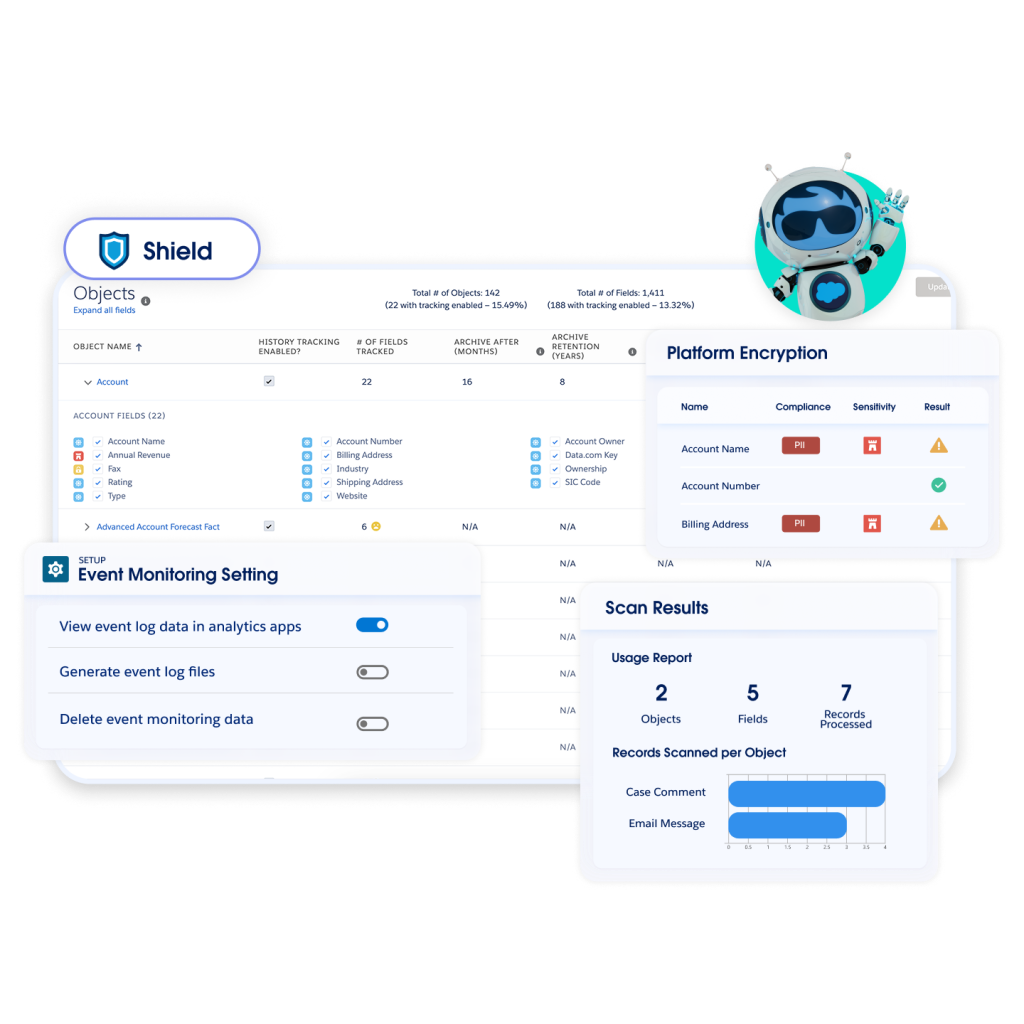
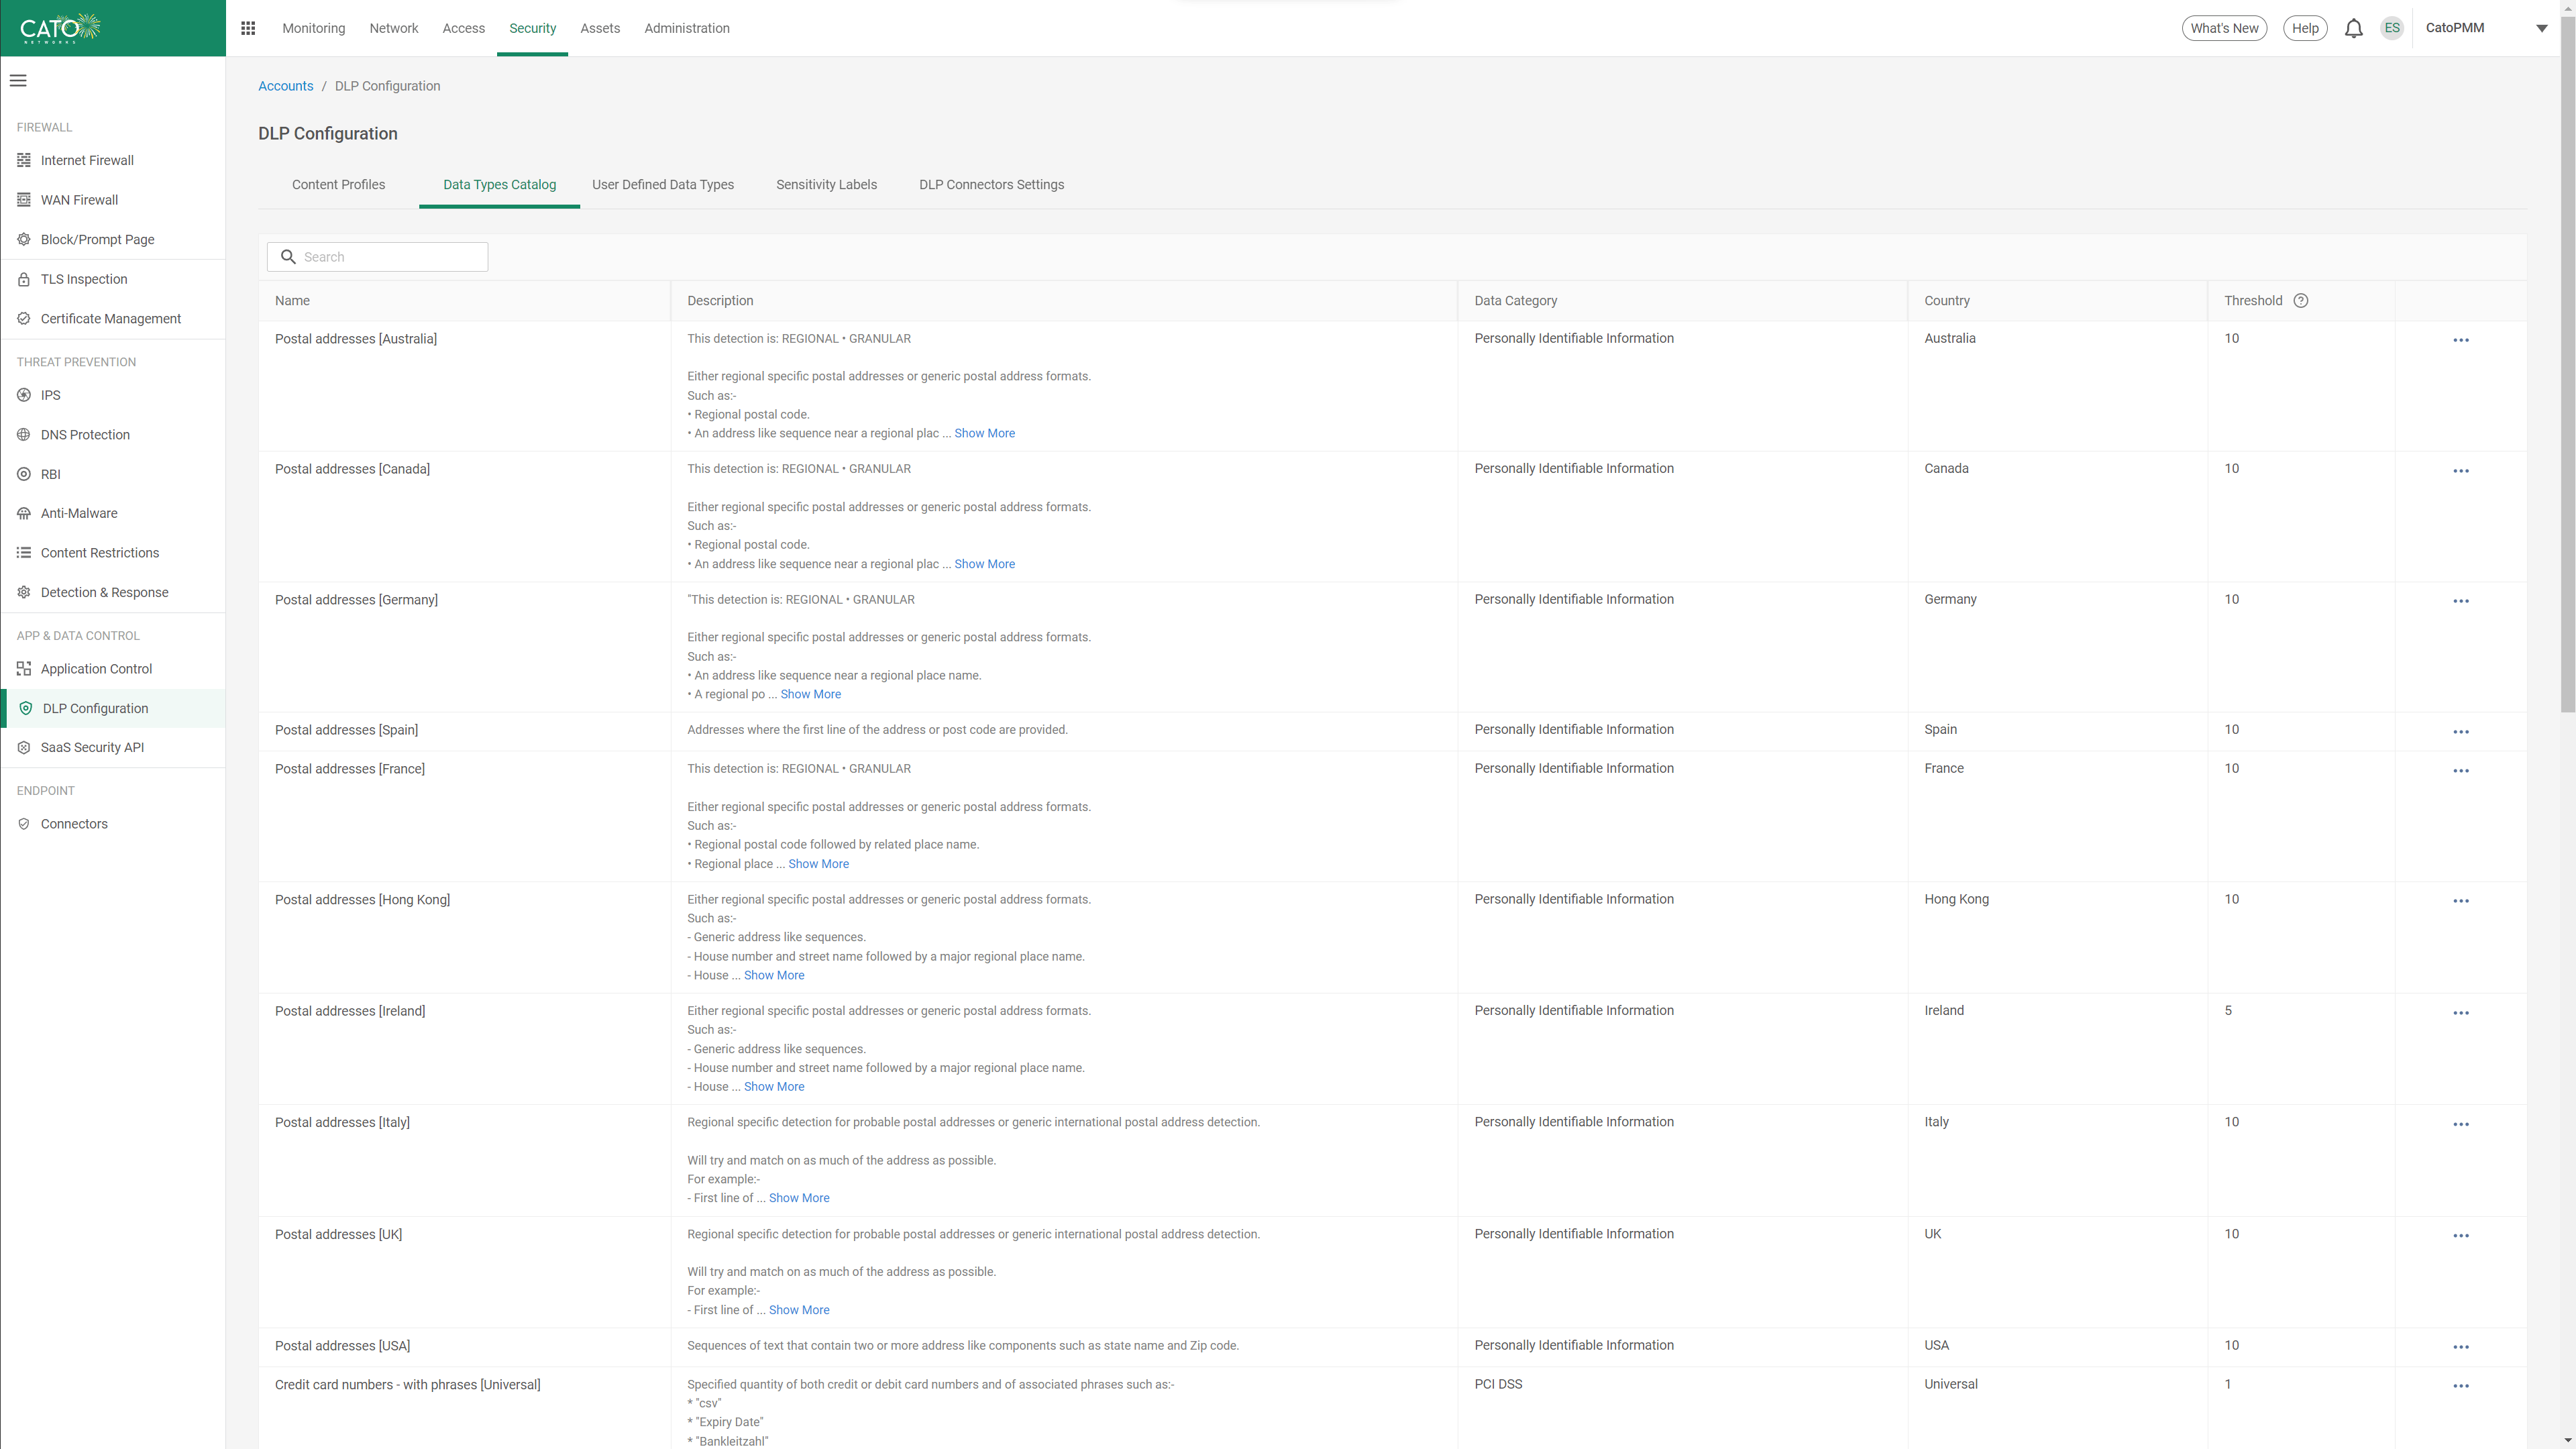
The core problem DLP solves is the visibility and control gap created by modern digital workflows. As organizations migrate to the cloud and adopt hybrid work models, the traditional network perimeter has dissolved. Sensitive data—such as Personally Identifiable Information (PII), Intellectual Property (IP), and financial records—now resides on laptops, mobile devices, cloud storage, and SaaS applications. Without DLP, organizations are blind to how this data is accessed or shared. The software identifies sensitive data through content analysis (e.g., matching credit card patterns or keywords) and contextual analysis (e.g., user behavior or file origin), then automatically applies remediation actions like encryption, blocking, or quarantining. This capability is critical not just for preventing financial loss and reputational damage, but for meeting stringent regulatory requirements such as GDPR, HIPAA, and PCI-DSS.
Who uses DLP software? Historically, it was the domain of large enterprises with dedicated security operations centers (SOCs). Today, the user base has democratized. Small and mid-sized businesses (SMBs) increasingly deploy lightweight or cloud-native DLP solutions to protect proprietary data and client lists. In regulated industries, compliance officers and data privacy managers rely on DLP dashboards to audit data handling practices and demonstrate due diligence to auditors. From a C-level perspective, DLP is a risk management instrument; for IT and security teams, it is a daily operational tool to triage alerts and educate users on safe data practices. The strategic importance of DLP has elevated from a "nice-to-have" insurance policy to a fundamental component of the Zero Trust security architecture, where no user or device is trusted implicitly with sensitive data access.
History of Data Loss Prevention Software
The trajectory of the Data Loss Prevention market is a study in the evolving value of data itself. In the 1990s and early 2000s, information security was synonymous with infrastructure security. Organizations focused on firewalls and antivirus software to build higher walls around their networks. However, a critical gap emerged: while the walls were high, the gates were wide open for insiders to walk out with proprietary information. This era’s "data protection" was largely limited to basic access controls and database security, which failed to address unstructured data like emails, documents, and spreadsheets. The gap between infrastructure security and data visibility birthed the DLP category.
The mid-2000s marked the first major wave of DLP innovation, characterized by the rise of standalone, "best-of-breed" vendors. These early pioneers introduced the concept of content-aware inspection, moving beyond simple file extension blocking to deep packet inspection that could read the text inside a document. This period saw a flurry of activity as organizations realized that their greatest risks often sat in the cubicle next door—the "accidental insider" emailing the wrong file, or the departing employee downloading a customer list. This realization triggered a massive wave of market consolidation between 2006 and 2010. Major security incumbents, recognizing the threat to their dominance, aggressively acquired these standalone DLP startups. This consolidation shaped the landscape we see today, where DLP features are often bundled into broader endpoint protection platforms or security suites rather than sold as disparate tools.
The 2010s brought the cloud revolution and a seismic shift in buyer expectations. The "lift and shift" of on-premises servers to the cloud rendered traditional network-based DLP appliances less effective. Data was no longer passing through a single corporate gateway; it was moving directly from a user’s laptop to a cloud application. This necessitated the rise of Cloud Access Security Brokers (CASB) and cloud-native DLP solutions that could hook into APIs of SaaS platforms. During this phase, the market also saw a shift in philosophy from "blocking" to "monitoring." Early DLP implementations were notorious for their heavy-handed "block" policies that stifled productivity—stopping a CEO from sending a critical presentation because it contained a phone number. By the late 2010s and early 2020s, the market matured into "adaptive" and "people-centric" DLP. Modern solutions began prioritizing user behavior analytics (UBA) to understand intent, distinguishing between a legitimate business process and a theft attempt. Today, the evolution continues as the market integrates Artificial Intelligence to classify unstructured data with near-human accuracy, moving the industry from simple database matching to actionable, risk-based intelligence.
What to Look For
Evaluating Data Loss Prevention software requires a disciplined focus on accuracy and workflow integration rather than just a checklist of features. The most critical evaluation criterion is the efficacy of detection techniques. Basic tools rely on "regular expressions" (Regex) to find patterns like social security numbers, which often leads to high false positive rates—flagging a product SKU as a credit card number, for instance. Superior solutions employ advanced techniques like Exact Data Matching (EDM) or Index Document Matching (IDM), which fingerprint specific database records or document templates to ensure that a match is genuinely sensitive corporate data. Buyers must verify that the solution can inspect complex file types, including CAD drawings for manufacturers or media files for creative agencies, and can perform Optical Character Recognition (OCR) to catch sensitive data embedded in scanned PDFs or images.
Red flags and warning signs often appear during the Proof of Concept (POC) phase. A major warning sign is a system that requires weeks of "tuning" before it can be turned on without overwhelming the security team. If a vendor cannot demonstrate value within days using out-of-the-box policies, it suggests their classification engine is outdated or overly reliant on manual configuration. Another red flag is a "heavy agent." Endpoint DLP relies on software agents installed on laptops; if these agents consume significant CPU resources, they will slow down employee machines, leading to user revolt and IT support tickets. Furthermore, be wary of vendors who gloss over macOS or Linux support; many legacy tools treat non-Windows operating systems as second-class citizens, leaving blinding gaps in coverage for creative or engineering teams.
When engaging with vendors, asking the right questions can reveal the maturity of their product.
- "How does your solution handle encrypted traffic?" (Crucial, as most modern web traffic is encrypted via HTTPS; if the tool can't inspect SSL/TLS traffic, it is effectively blind).
- "Can you walk me through the workflow for a false positive?" (You want to see how easy it is for an analyst to dismiss an alert and tune the policy so it doesn't happen again).
- "Does the system support 'user justification'?" (This feature allows a user to override a block by providing a business reason, which balances security with productivity).
- "How is your licensing structured regarding data retention?" (Some cloud DLP vendors charge extra for storing log data beyond a short window, complicating compliance audits).
Industry-Specific Use Cases
Retail & E-commerce
For retailers, the primary currency of trust is the Payment Card Industry (PCI) data. Retail DLP solutions must prioritize the protection of credit card numbers (PAN) and authentication data across a sprawling network of Point-of-Sale (POS) systems and e-commerce backends. Unlike a corporate office, a retail environment involves thousands of transient endpoints (registers, handheld scanners) that may be on older operating systems. [1]
Evaluation priorities here shift heavily toward compliance reporting and endpoint resource efficiency. Retailers operate on thin margins and often use lower-spec hardware for POS terminals; a heavy DLP agent that causes transaction lag is unacceptable. Furthermore, the rise of franchise models means data must be segmented—store managers should only see their store’s data, while corporate sees the aggregate. A DLP tool for retail must support robust role-based access control (RBAC) to reflect this hierarchy. Unique considerations also include inventory data protection; leakage of pricing strategies or upcoming promotion schedules to competitors can be as damaging as a PII breach. [2]
Healthcare
The healthcare sector faces the highest average cost of a data breach, reaching nearly $9.77 million per incident according to recent reports [3]. The focus here is strictly on Protected Health Information (PHI) and maintaining HIPAA compliance. Unlike financial data, which is structured (numbers), health data is often unstructured—doctor's notes, X-ray images, and scanned insurance forms. Therefore, healthcare buyers must prioritize DLP solutions with advanced Optical Character Recognition (OCR) and Natural Language Processing (NLP) capabilities to identify patient names buried in scanned PDFs or image files.
Unique to healthcare is the tension between data security and patient care. A "block" policy that prevents a doctor from emailing a patient record to a specialist could delay critical treatment. Consequently, healthcare organizations often favor DLP configurations that emphasize "monitoring and coaching" over outright blocking, or that use intelligent encryption that allows the email to be sent but ensures only the intended recipient can open it. Device control is also paramount, as medical environments are rife with shared workstations and USB usage for medical devices. [4]
Financial Services
Financial institutions are the original power users of DLP, driven by regulations like GLBA, SOX, and regional banking laws. The use case here extends beyond simple PII protection to complex insider threat detection. Banks worry about traders taking proprietary algorithms or loan officers downloading client portfolios before defecting to a competitor. [5]
Evaluation priorities include exact data matching (EDM) capable of scaling to millions of customer records without performance degradation. False positives in finance are costly; blocking a legitimate multi-million dollar wire transfer instruction due to a DLP error can cause significant business friction. Financial firms also require deep integration with communication compliance tools to monitor chat logs (e.g., Bloomberg terminals, Slack) for anti-money laundering (AML) indicators or insider trading collusion, blending DLP with communication surveillance. [6]
Manufacturing
In manufacturing, the crown jewels are not credit card numbers but Intellectual Property (IP)—CAD files, chemical formulas, and supply chain pricing lists. The theft of IP is a leading concern, often involving state-sponsored actors or corporate espionage. Standard DLP that looks for "social security numbers" is useless here. Manufacturing buyers need DLP that understands file fingerprinting for non-text files (like 3D design files) and can detect "low and slow" data exfiltration where small amounts of data are leaked over time to avoid detection.
A unique consideration is the Operational Technology (OT) environment. Manufacturing floors are increasingly connected (Industry 4.0), and proprietary data flows between the corporate IT network and the factory OT network. DLP solutions must be able to monitor these gateways without interfering with industrial control systems (ICS). Additionally, supply chain collaboration requires sharing sensitive specs with third-party vendors; DLP here must support "Digital Rights Management" (DRM) integration to ensure that a file sent to a supplier cannot be opened after the contract expires. [7]
Professional Services
Law firms, consultancies, and accounting firms hold the secrets of *other* companies. Their reputation is their product, and a breach can be an existential threat. The unique challenge for professional services is the client-centric data structure. A law firm might need to block data from Client A being sent to Client B, even though both are legitimate business contacts. This requires a DLP solution with sophisticated "ethical wall" capabilities.
Evaluation priorities focus on mobility and transient access. Consultants are road warriors (physically or virtually), constantly connecting from hotel Wi-Fi or client networks. The DLP agent must be robust enough to enforce policies when the device is off the corporate VPN. Furthermore, the "deal room" scenario—where sensitive M&A documents are shared temporarily—requires DLP that integrates tightly with collaboration platforms like Microsoft Teams or specialized virtual data rooms to prevent unauthorized downloading or printing of view-only documents. [8]
Emerging Trends and Contrarian Take
Looking toward 2025-2026, the dominant trend is the convergence of DLP into Data Security Posture Management (DSPM). Traditional DLP is reactive (scanning data as it moves), whereas DSPM is proactive (finding shadow data where it lives). The integration of these two disciplines allows for a holistic view: discovering sensitive data in a forgotten cloud bucket and automatically applying a DLP policy to it. Another explosive trend is the protection against "Shadow AI"—employees pasting sensitive corporate code or strategy into public GenAI tools like ChatGPT. DLP vendors are rapidly rolling out features to "sanitize" inputs to Large Language Models (LLMs) in real-time.
Contrarian Take: The standalone DLP market is dying, and that is a good thing. For years, vendors sold the lie that software could solve a data culture problem. The truth is that most mid-market businesses would get more ROI from hiring one dedicated Data Governance officer than buying any DLP platform. Tools are useless without someone who understands *what* data matters. Furthermore, the obsession with "preventing" loss is shifting; in a world of decentralized, encrypted, and fragmented data, "Loss Prevention" is becoming impossible. The future isn't keeping data in; it's making data useless to steal via ubiquitous encryption and rights management. The "perimeter" is now the file itself, not the network.
Common Mistakes
The path to DLP failure is paved with good intentions and bad configurations.
Over-blocking on Day One: As discussed, moving to enforcement mode before understanding business workflows is the fastest way to lose executive support.
 B